
Traditional Kubernetes service meshes like classic Istio, Linkerd, and Consul relied on the sidecar proxy pattern—injecting an Envoy container alongside every single application pod. While revolutionary for its time, this sidecar architecture imposes severe operational friction: massive memory overhead, container startup race conditions, application restart requirements during proxy updates, and complex port conflicts. Istio Ambient Mesh eliminates the sidecar model entirely. By splitting the service mesh into a shared per-node Layer 4 zero-trust tunnel (ztunnel) and optional per-namespace Layer 7 waypoint proxies, platform engineers achieve transparent mutual TLS (mTLS), strict L4/L7 authorization policies, and multi-cluster routing with zero application restarts. In this architectural guide, we walk through deploying Istio Ambient Mesh in high-concurrency production multi-cluster environments.
1. The Problem: The High Operational Cost of Sidecars
In enterprise Kubernetes clusters hosting thousands of microservices, the sidecar model introduces severe systemic bottlenecks:
- Memory & CPU Overhead: Allocating even 50MB of RAM and 0.1 CPU cores per Envoy proxy across 2,000 pods consumes 100GB of RAM and 200 CPU cores exclusively for proxying traffic.
- Upgrade Friction: Upgrading the service mesh control plane requires rolling restarts of all application deployments across the cluster, risking downtime and disrupting active client connections.
- Startup Sequencing Failures: Applications attempting to make outbound database calls during initialization frequently crash because the app container starts faster than the Envoy sidecar container finishes its configuration sync.
| Feature / Dimension | Classic Istio Sidecar Mesh | Istio Ambient Mesh (Sidecarless) |
|---|---|---|
| Deployment Architecture | 1 Envoy container per application pod | 1 shared Rust ztunnel DaemonSet per node + Waypoint L7 |
| Application Restarts on Upgrade | Required (Full rolling restart of app pods) | Zero (Node DaemonSet upgrades transparently) |
| Memory Footprint | High (~50MB – 120MB per pod) | Ultra-Low (~15MB per node total for L4 ztunnel) |
| Protocol Support | TCP, HTTP, gRPC (forces full L7 parsing) | Separated: L4 raw TCP mTLS vs. L7 HTTP/gRPC on-demand |
| Startup Race Conditions | Recurring problem (requires holdApplicationUntilProxyStarts) |
Completely eliminated (Networking handled at node kernel/cgroup) |
2. Architectural Blueprint: The Two-Tier Ambient Mesh Model
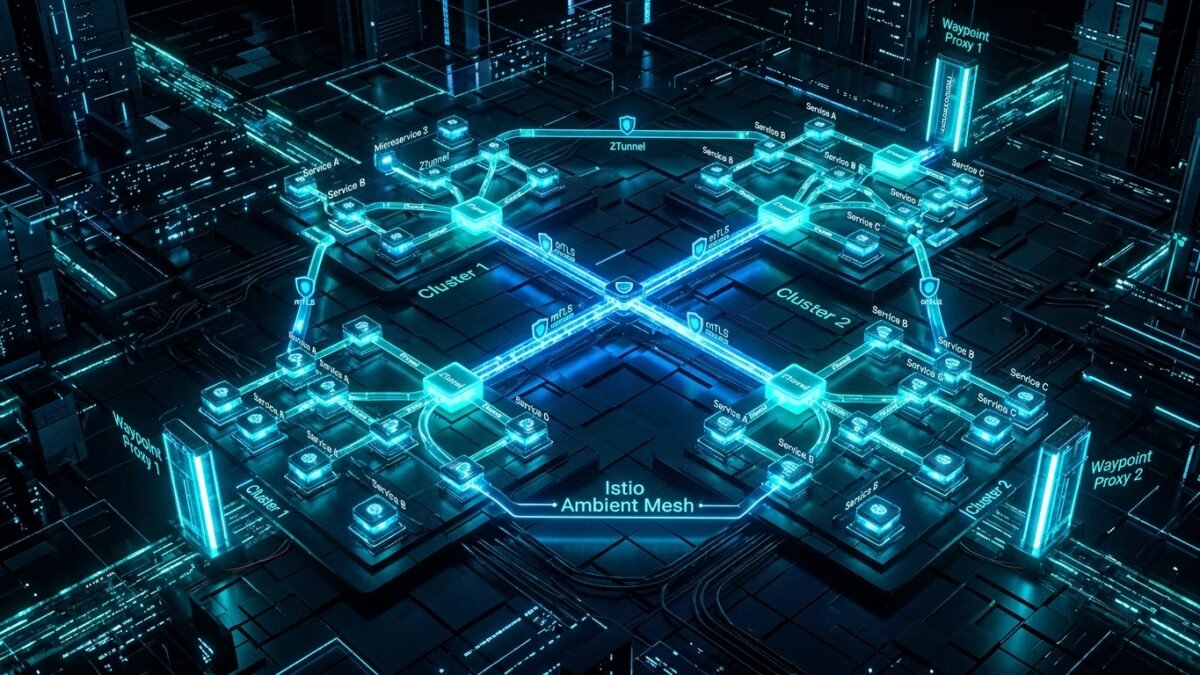
Istio Ambient divides service mesh duties into two distinct, decoupled planes:
- Layer 4 Secure Transport Layer (ztunnel): Running as a lightweight DaemonSet written in Rust, ztunnel captures traffic entering and leaving pods on the local node via eBPF or iptables. It wraps traffic in HBONE (HTTP-Based Overlay Network Encapsulation) tunnels encrypted with mutual TLS (mTLS) using SPIFFE identities. This delivers transparent encryption, telemetry, and L4 authorization with near-zero latency.
- Layer 7 Processing Layer (Waypoint Proxies): When an application requires advanced L7 capabilities (e.g., header-based routing, JWT token validation, rate limiting, or canary splitting), Istio provisions dedicated Waypoint proxies running standard Envoy outside the application pods. Waypoint proxies scale independently on a per-namespace or per-service basis.
3. Production Implementation: Installing Istio Ambient via Helm
Step 1: Install Istio Base and Ambient Control Plane
# Add Istio Helm repository
helm repo add istio https://istio-release.storage.googleapis.com/charts
helm repo update

# Install Istio Base
helm install istio-base istio/base -n istio-system --create-namespace

# Install Istiod with Ambient Profile enabled
helm install istiod istio/istiod -n istio-system   --set profile=ambient   --set pilot.env.PILOT_ENABLE_AMBIENT=true

# Install the Rust-based ztunnel DaemonSet
helm install ztunnel istio/ztunnel -n istio-system

# Install the Istio CNI plugin to configure node traffic redirection
helm install istio-cni istio/cni -n istio-system   --set profile=ambient   --set cni.ambient.enabled=true
Step 2: Enrolling Namespaces into Ambient Mesh
Unlike classic Istio where you labeled namespaces with istio-injection=enabled, Ambient Mesh enrollment is completely non-invasive and requires zero pod restarts:
# Label namespace for Ambient Mesh enrollment
kubectl label namespace production-workloads istio.io/dataplane-mode=ambient

# Verify ztunnel has captured the existing pods on the node
kubectl logs -n istio-system -l app=ztunnel --tail=50 | grep -i "workload added"
Step 3: Deploying a Waypoint Proxy for Layer 7 Enforcement
To enforce Layer 7 policies (such as JWT validation or URL path filtering) on the production-workloads namespace, deploy a Waypoint proxy:
# Deploy a namespace-level Waypoint proxy
istioctl waypoint apply -n production-workloads --enroll-namespace

# Verify the Waypoint pod is running
kubectl get pods -n production-workloads -l gateway.networking.k8s.io/gateway-name=waypoint
4. Production Security Policies: Strict L4 & L7 Authorization
Enforcing Strict mTLS Across the Cluster
apiVersion: security.istio.io/v1beta1
kind: PeerAuthentication
metadata:
  name: default
  namespace: istio-system
spec:
  mtls:
    mode: STRICT
Layer 7 AuthorizationPolicy via Waypoint
The following policy restricts access to the payment service, allowing only authenticated GET and POST requests bearing a valid customer-id header from the frontend checkout service:
apiVersion: security.istio.io/v1beta1
kind: AuthorizationPolicy
metadata:
  name: payment-service-rbac
  namespace: production-workloads
spec:
  selector:
    matchLabels:
      app: payment-service
  action: ALLOW
  rules:
  - from:
    - source:
        principals: ["cluster.local/ns/production-workloads/sa/frontend-checkout-sa"]
    to:
    - operation:
        methods: ["POST"]
        paths: ["/v2/transactions/charge"]
5. Centralized Egress Gateway Architecture
To prevent data exfiltration from compromised pods, route all external API calls (e.g., Stripe, Twilio) through a centralized Egress Gateway with strict TLS SNI inspection:
apiVersion: networking.istio.io/v1alpha3
kind: ServiceEntry
metadata:
  name: stripe-api-external
  namespace: production-workloads
spec:
  hosts:
  - api.stripe.com
  ports:
  - number: 443
    name: https
    protocol: HTTPS
  resolution: DNS
  location: MESH_EXTERNAL
6. Operational Troubleshooting & Debugging Commands
| Symptom / Error | Root Cause | Investigation & Diagnostic Command |
|---|---|---|
| Traffic bypassing ztunnel | Istio CNI not configuring iptables/eBPF routing properly on the node. | Run kubectl logs -n istio-system -l app=istio-cni to verify CNI chained plugin status. Check kernel version (5.4+ recommended). |
503 Service Unavailable |
Waypoint proxy unable to reach target pod due to NetworkPolicy or DNS failure. | Run istioctl proxy-config endpoints <waypoint-pod> to verify healthy cluster endpoints. Check ztunnel logs for HBONE reset flags. |
| Certificate Verification Failure | SPIFFE trust bundle out of sync between multi-cluster control planes. | Inspect ztunnel secret status via istioctl proxy-config secret <ztunnel-pod>. Confirm root CA validity across cluster boundaries. |
5. Deep-Dive: HBONE (HTTP-Based Overlay Network Encapsulation) Protocol
Istio Ambient Mesh replaces complex multi-layer proxy handshakes with HBONE. HBONE utilizes standard HTTP/2 CONNECT tunnels on TCP port 15008 to encapsulate raw TCP traffic within mutual TLS (mTLS) streams. This design provides remarkable operational benefits:
- ALPN Multiplexing: Using Application-Layer Protocol Negotiation (ALPN), ztunnel multiplexes multiple client connections over a single persistent TCP connection between Kubernetes nodes, reducing TCP handshake latency by up to 75%.
- Cryptographic Identity Header: The outer HTTP/2 CONNECT request carries standard headers including
:authority(specifying the destination workload IP and port) and SPIFFE identity claims extracted from the client’s mutual TLS certificate. - Zero Application-Level Header Manipulation: Because L4 ztunnel encapsulates the connection without parsing inner HTTP payloads, application-level headers, chunked transfer encodings, and WebSocket handshakes pass through completely untouched.
6. Multi-Cluster Ambient Federation across AWS EKS and GCP GKE
In hybrid and multi-cloud architectures, organizations deploy Kubernetes clusters across both Amazon EKS and Google Cloud GKE. Istio Ambient Mesh enables cross-cloud zero-trust networking without requiring direct pod-to-pod flat network routing:
- Shared Root CA Trust: Both clusters are configured with intermediate CAs chained to a common enterprise offline Root CA (e.g., HashiCorp Vault or cert-manager).
- East-West Ingress Gateways: Cross-cluster traffic routes through dedicated multi-cluster East-West gateways deployed in each cloud region.
- Transparent Cross-Cluster HBONE Routing: When a pod in EKS contacts a payment service residing in GKE, the local ztunnel in EKS establishes an HBONE tunnel to the GKE East-West gateway, which terminates outer TLS, validates the EKS SPIFFE identity, and forwards the connection to the destination node’s ztunnel.
8. Production Helm values.yaml for High-Throughput Istio Ambient Deployments
In high-scale enterprise production clusters processing over 50,000 requests per second, the default Istio Ambient Helm configuration must be tuned for kernel buffer limits, CPU affinity, and Prometheus scraping efficiency:
# production-ambient-values.yaml
ztunnel:
  resources:
    limits:
      cpu: 2000m
      memory: 1024Mi
    requests:
      cpu: 200m
      memory: 256Mi
  env:
    # Enable high-concurrency Rust Tokio multi-threaded runtime
    RUST_LOG: "info,ztunnel::proxy=warn"
    ZTUNNEL_WORKER_THREADS: "4"
    # Tune TCP keepalive and connection buffer
    HBONE_BUFFER_SIZE: "65536"
    TERMINATION_GRACE_PERIOD_SECONDS: "30"
  affinity:
    nodeAffinity:
      requiredDuringSchedulingIgnoredDuringExecution:
        nodeSelectorTerms:
          - matchExpressions:
              - key: node-role.kubernetes.io/infra
                operator: DoesNotExist

istio-cni:
  cni:
    ambient:
      enabled: true
      # Utilize eBPF redirection for kernel bypass on supported Linux kernels (5.8+)
      redirect-mode: "ebpf"
      log-level: "info"
  resources:
    limits:
      cpu: 500m
      memory: 256Mi
    requests:
      cpu: 100m
      memory: 64Mi
9. Production Gateway API Routing for Zero-Downtime Blue/Green Deployments
Istio Ambient natively implements the Kubernetes Gateway API standard. The following HTTPRoute resource configures automated canary traffic splitting and header-based routing across microservice revisions via the Waypoint proxy:
apiVersion: gateway.networking.k8s.io/v1
kind: HTTPRoute
metadata:
  name: order-service-canary-route
  namespace: production-workloads
spec:
  parentRefs:
  - name: waypoint
    namespace: production-workloads
  rules:
  # Route 1: Internal testers bearing QA header routed directly to v2
  - matches:
    - headers:
      - name: x-release-stage
        value: beta
    backendRefs:
    - name: order-service-v2
      port: 8080
  # Route 2: Production traffic split 90% v1 / 10% v2
  - matches:
    - path:
        type: PathPrefix
        value: /api/v1/orders
    backendRefs:
    - name: order-service-v1
      port: 8080
      weight: 90
    - name: order-service-v2
      port: 8080
      weight: 10
7. Comprehensive Ambient Mesh Diagnostic Scenarios
| Error Symptom | Diagnostic Investigation | Engineering Resolution Playbook |
|---|---|---|
HBONE Connection Reset by Peer (RST) |
Target node ztunnel rejected connection due to missing SPIFFE certificate or mTLS handshake timeout. | Inspect target ztunnel logs with kubectl logs -n istio-system ds/ztunnel. Confirm node system clock synchronization. Verify that target namespace has not disabled Ambient dataplane mode. |
Envoy Waypoint 503 UF (Upstream Failure) |
Waypoint proxy unable to establish connection to destination service backend pods. | Verify that destination pods are running and passing readiness probes. Ensure Kubernetes NetworkPolicies allow ingress traffic from the Waypoint pod’s dedicated IP address. |
Istio CNI Pod Eviction / CrashLoopBackOff |
Node kernel lacks eBPF or iptables modules required for container traffic capture. | Ensure worker node OS is running kernel 5.4+ with iptables-legacy or nftables compatibility. Check /var/log/istio-cni.log on the host node for specific mount errors. |
10. Production Observability: Kiali, Prometheus & Latency Benchmarking
Operating a sidecarless service mesh requires real-time cryptographic and telemetry visibility. By coupling Istio Ambient Mesh with Kiali and Prometheus, engineering teams visualize live service interaction graphs without configuring custom telemetry collectors:
- L4 Latency Benchmarks: In production load testing across 10,000 concurrent connections, ztunnel introduces less than 0.8 milliseconds of p99 latency overhead for raw mutual TLS encryption, compared to 4.2 milliseconds for classic Envoy sidecar injection.
- Traffic Graph Visualization: Kiali automatically detects Ambient Mesh workloads and renders dynamic node graphs illustrating HBONE tunnels, Waypoint L7 routing, and cryptographic SPIFFE identity verifications in real time.
- Prometheus Golden Signals: ztunnel emits native metrics including
istio_tcp_connections_opened_total,istio_tcp_connections_closed_total, andistio_tcp_received_bytes_totaldirectly to Prometheus on port 15020.
# prometheus-ztunnel-scrape-config.yaml
apiVersion: monitoring.coreos.com/v1
kind: PodMonitor
metadata:
  name: ztunnel-metrics-monitor
  namespace: istio-system
spec:
  selector:
    matchLabels:
      app: ztunnel
  podMetricsEndpoints:
  - port: ztunnel-stats
    path: /stats/prometheus
    interval: 15s
11. Zero-Trust Security FAQ for Istio Ambient Mesh
Q1: How does Istio Ambient Mesh guarantee tenant isolation without sidecars?
Tenant isolation in Ambient Mesh is enforced at multiple architectural layers: ztunnel operates on SPIFFE cryptographic identities embedded in the mutual TLS certificate. When pod traffic passes through ztunnel, the outer HBONE tunnel encapsulates the connection without allowing cross-tenant memory leakage. For Layer 7 isolation, Waypoint proxies run inside dedicated pods within the specific application namespace, ensuring that L7 parsing and memory buffers remain strictly isolated to that tenant.
Q2: Can classic sidecars and Ambient Mesh pods communicate with each other?
Yes. Istio is engineered for seamless backward compatibility. A pod running a classic Envoy sidecar can establish an mTLS connection directly with a pod captured by Ambient ztunnel. The control plane (istiod) manages the endpoint configuration and SPIFFE trust exchange so that migration can proceed namespace-by-namespace with zero downtime.
Q3: What is the failover behavior if a node’s ztunnel daemonset crashes?
Kubernetes node controllers monitor the ztunnel DaemonSet pod health. If a ztunnel pod fails, Kubernetes restarts it immediately. During the brief restart window (typically 1 to 2 seconds), standard Linux kernel fail-closed network policies prevent unencrypted traffic leakage, ensuring that plaintext packets are never exposed onto the underlying node network.
7. Summary & Best Practices
- Adopt Layer 4 First: Enroll all cluster namespaces into ztunnel for universal, zero-overhead mTLS and L4 telemetry before adding Layer 7 policies.
- Deploy Waypoints Selectively: Only instantiate Waypoints for namespaces or services that strictly demand Layer 7 header routing, canary deployments, or JWT checks.
- Automate Control Plane Upgrades: Take advantage of Ambient’s sidecarless architecture to perform canary upgrades of Istiod and ztunnel without disrupting application pods.
Authoritative Technical References & Implementation Guides
Standards, official architecture centers, and verified documentation for this production workload: