
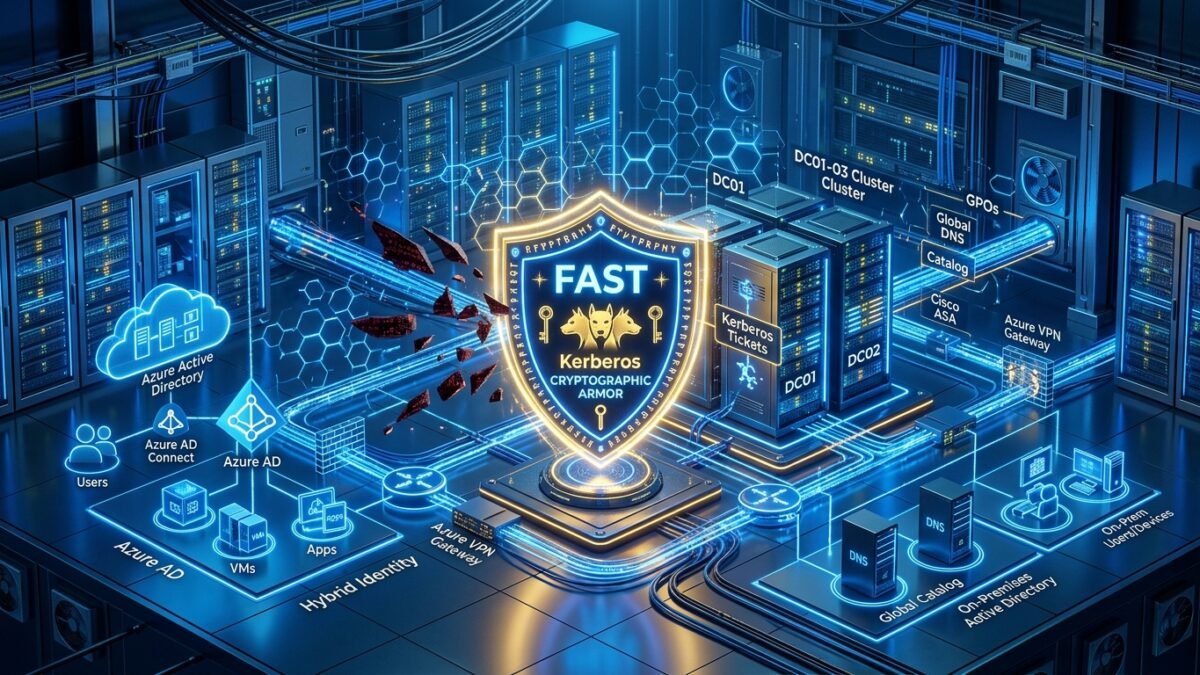
Active Directory remains the primary target for advanced threat actors seeking enterprise domain compromise. While modern cloud workloads have transitioned toward OAuth 2.0 and SAML, on-premises Domain Controllers (DCs) continue to process millions of legacy Kerberos tickets daily. Attack vectors like Kerberoasting, AS-REP Roasting, and Pass-the-Hash exploit architectural defaults that have persisted since Windows Server 2003. In this production engineering guide, we dissect the implementation of Kerberos Armoring—technically known as Flexible Authentication Secure Tunneling (FAST)—alongside the Protected Users Security Group, Privilege Access Workstations (PAWs), and Group Managed Service Account (gMSA) migrations to construct an impenetrable Tier-0 defensive perimeter.
1. The Problem: Kerberos Architectural Flaws Exploited in the Wild
The standard Kerberos v5 protocol exchange is vulnerable to offline cryptanalysis if legacy compatibility is prioritized over strict cryptographic controls:
- AS-REP Roasting: When user accounts have
Do not require Kerberos preauthenticationenabled, an unauthenticated attacker can request an encrypted Ticket Granting Ticket (TGT) directly from the KDC and brute-force the password hash offline without triggering lockout counters. - Kerberoasting: Any domain user can request a service ticket (TGS) for any Service Principal Name (SPN). Because the ticket is encrypted using the service account’s NTLM/RC4 hash, attackers capture the ticket from memory and crack weak service passwords offline using hashcat or John the Ripper.
- Credential Caching & Pass-the-Hash: Domain administrators logging into Tier-1 or Tier-2 workstations leave credentials (NTLM hashes, Kerberos TGTs) cached in the Local Security Authority Subsystem Service (LSASS) memory space, allowing attackers wielding Mimikatz to escalate instantly to Enterprise Admin.
| Attack Vector | Vulnerable Default Configuration | Hardened Tier-0 Mitigation |
|---|---|---|
| Kerberoasting | User accounts running services with RC4/AES128 SPNs | Migrate to Group Managed Service Accounts (gMSA) + 128-char passwords |
| AS-REP Roasting | Pre-authentication disabled on legacy service accounts | Enforce Kerberos Armoring (FAST) + Mandatory Pre-Auth |
| Pass-the-Hash / LSASS Dump | Admins logging into user workstations with NTLM cached | Protected Users Security Group + Credential Guard + PAW |
| Silver Ticket Attacks | Stale machine account passwords or static SPN keys | Automated password rotation via gMSA + AES-256 Kerberos Only |
| Golden Ticket Attacks | Single KRBTGT account password never rotated | Automated Dual KRBTGT Password Reset Script (every 90 days) |
2. Architectural Blueprint: Flexible Authentication Secure Tunneling (FAST)
Kerberos Armoring (FAST, specified in RFC 6113) solves a fundamental weakness in Kerberos pre-authentication: the initial AS-REQ message containing pre-authentication data is unarmored and exposed to network sniffing and tampering. FAST wraps pre-authentication exchanges inside an encrypted cryptographic tunnel established using the machine’s credential (the computer account’s secret key).
The FAST Handshake Mechanics
- Computer Authentication: The client machine initiates an exchange with the KDC using its computer account credentials, establishing a cryptographic session key.
- Armor Establishment: When a user logs onto that machine, the client software generates an armored
AS-REQ. The user’s pre-authentication data is encrypted with the computer account’s session key. - Tamper-Proof KDC Validation: The Domain Controller validates that the user request originated from an authorized, domain-joined machine whose machine ticket is valid. Man-in-the-Middle spoofing and offline ticket capture are cryptographically blocked.
3. Production Implementation: Deploying Kerberos Armoring & Claims via GPO
Phase 1: Configure Domain Controller Policy for Kerberos Armoring
Kerberos Armoring requires a minimum Domain Functional Level of Windows Server 2012 R2 (recommended: Windows Server 2019/2022). To enable FAST across all Domain Controllers:
# 1. Enable KDC Support for Claims, Compound Authentication and Kerberos Armoring
# Location: Computer Configuration > Policies > Administrative Templates > System > KDC
# Setting: 'KDC support for claims, compound authentication and Kerberos armoring'

$GpoName = "Tier0-DomainControllers-Kerberos-Hardening"
New-GPO -Name $GpoName -Comment "Enforces Kerberos Armoring FAST and Claims Support"
Set-GPRegistryValue -Name $GpoName `
    -Key "HKLMSoftwareMicrosoftWindowsCurrentVersionPoliciesSystemKDC" `
    -ValueName "KdcArmoringMode" `
    -Type DWord `
    -Value 2 # 2 = Supported (Permits unarmored clients during migration, protects armored)

Write-Host "KDC Armoring GPO setting successfully written." -ForegroundColor Green
Phase 2: Configure Client Computer Policy for Kerberos Armoring
Client workstations and member servers must be instructed to request Kerberos armor when contacting the KDC:
# 2. Configure Client Workstations to enforce Kerberos Armoring
# Location: Computer Configuration > Policies > Administrative Templates > System > Kerberos
# Setting: 'Kerberos client support for claims, compound authentication and Kerberos armoring'

$ClientGpoName = "Baseline-Workstations-Kerberos-Armor"
New-GPO -Name $ClientGpoName -Comment "Enables Kerberos FAST Armoring on domain workstations"
Set-GPRegistryValue -Name $ClientGpoName `
    -Key "HKLMSoftwareMicrosoftWindowsCurrentVersionPoliciesSystemKerberosParameters" `
    -ValueName "EnableCbacAndArmor" `
    -Type DWord `
    -Value 1 # 1 = Enabled

Write-Host "Client Kerberos Armoring GPO configured." -ForegroundColor Green
4. Hardening Tier-0 Identities: The Protected Users Security Group
Introduced in Windows Server 2012 R2, the Protected Users built-in security group triggers non-configurable security restrictions for any member account:
- No NTLM Authentication: NTLM hashes are never cached in memory; attempts to authenticate via NTLM fail immediately.
- Strict Kerberos Encryption: DES and RC4 encryption types are disabled; Kerberos pre-authentication is strictly enforced using AES-128 or AES-256.
- No Ticket Granting Ticket (TGT) Renewal: TGT lifetime is capped at 4 hours and cannot be renewed; sessions terminate cleanly.
- No Credential Delegation: Unconstrained and constrained delegation are disabled, preventing token relay attacks.
# Add All Tier-0 Enterprise and Domain Admins to Protected Users
Import-Module ActiveDirectory

$Tier0Admins = @("svc-da-backup", "admin-shivam", "admin-tier0-audit")

foreach ($Admin in $Tier0Admins) {
    Add-ADGroupMember -Identity "Protected Users" -Members $Admin -Confirm:$false
    Write-Host "User $Admin enrolled in Protected Users group." -ForegroundColor Yellow
}

# Verify Membership
Get-ADGroupMember -Identity "Protected Users" | Select-Object Name, SamAccountName
5. Group Managed Service Accounts (gMSA) Migration
Service accounts configured with static passwords represent the single largest Kerberoasting attack surface in legacy Active Directory. Migrating them to gMSAs completely eliminates manual password management by delegating 128-character complex password rotation to Domain Controllers every 30 days.
# Step 1: Create KDS Root Key (Required once per forest)
# Note: In production, key becomes effective after 10 hours to allow multi-site replication
Add-KdsRootKey -EffectiveImmediately

# Step 2: Provision gMSA for Enterprise SQL Server Cluster
New-ADServiceAccount -Name "gmsa-sql-prod" `
    -DNSHostName "gmsa-sql-prod.contoso.com" `
    -PrincipalsAllowedToRetrieveManagedPassword "SQL-Cluster-Hosts" `
    -KerberosEncryptionType AES128,AES256 `
    -ServicePrincipalNames @("MSSQLSvc/sqlcluster.contoso.com:1433", "MSSQLSvc/sqlcluster.contoso.com")

Write-Host "gMSA gmsa-sql-prod provisioned with AES-256 encryption." -ForegroundColor Cyan
6. Operational Troubleshooting & Kerberos Error Codes
| Error Code | Diagnostic Description | Remediation & Architecture Fix |
|---|---|---|
KRB_AP_ERR_MODIFIED |
Checksum failed or SPN mapped to duplicate accounts. | Run setspn -X to locate and purge duplicate SPNs. Ensure client computer account is synchronized and machine password is valid. |
STATUS_NTLM_BLOCKED (0xC0000388) |
Protected Users member attempted to access an application that only supports legacy NTLM. | Upgrade the application to Kerberos SPN authentication. Never remove the admin from Protected Users to bypass this check. |
KDC_ERR_PREAUTH_FAILED (Event 4771) |
Kerberos pre-authentication failed (Code 0x18). | User entered incorrect password or automated task is using stale cached credentials. Check event log details for source IP address. |
KDC_ERR_ETYPE_NOTSUPP (Event 4768) |
Requested encryption type not supported by KDC. | The target account or Domain Controller has RC4 disabled and the client attempted an RC4 handshake. Enforce AES256 in user account attributes. |
5. Deep-Dive: Wireshark Packet Inspection of Kerberos Armoring (FAST)
To verify that Kerberos Armoring is actively protecting authentication exchanges across your corporate subnets, capture traffic on UDP/TCP port 88 during user logon and analyze the AS-REQ message in Wireshark:
- Unarmored Kerberos Request: The
padata(Pre-Authentication Data) array containsPA-ENC-TIMESTAMP(Type 2) encrypted directly with the user’s password hash. An attacker capturing this packet extracts the ciphertext and executes offline dictionary attacks against the user’s password. - Armored Kerberos FAST Request: The
padataarray containsPA-FX-FAST(Type 136). The user’s credentials are completely encapsulated inside an outer cryptographic armor envelope encrypted with the computer account’s long-term key. The innerAS-REQis invisible to network sniffers, rendering offline cracking attacks impossible.
6. Tier-0 Administrative Forest Architecture & Active Directory Modernization
Kerberos armoring must be deployed as part of an overarching Tier-0 isolation model. The Enterprise Access Model classifies identity infrastructure into three distinct security tiers:
- Tier 0 (Control Plane): Domain Controllers, PKI Certification Authorities, Entra Connect servers, ADFS farms, and Tier-0 Privileged Access Workstations (PAWs). Tier-0 credentials must never authenticate to Tier-1 or Tier-2 systems under any circumstances.
- Tier 1 (Management Plane): Enterprise member servers, SQL Server clusters, Hyper-V/VMware virtualization clusters, and enterprise storage arrays.
- Tier 2 (User & Endpoint Plane): End-user laptops, workstations, network printers, and mobile devices.
By enforcing the Protected Users group on all Tier-0 accounts and restricting logon rights via Group Policy Objects (Deny log on locally, Deny log on through Remote Desktop Services for Tier-0 accounts on all Tier-1 and Tier-2 systems), credential theft via Mimikatz and memory dumping is structurally eradicated.
8. Automated KRBTGT Dual-Run Password Reset Script
The KRBTGT account password encrypts all Kerberos Ticket Granting Tickets (TGTs) across the Active Directory forest. If an adversary compromises the KRBTGT password, they can forge Golden Tickets that grant permanent, untraceable Domain Admin access even after user passwords are changed. To invalidate forged tickets without causing service outages, Microsoft mandates a Dual-Run Reset spaced 10 to 24 hours apart:
# ==============================================================================
# Enterprise Tier-0 KRBTGT Password Reset & Replication Orchestrator
# Executes Step 1 of 2: First password reset with replication verification
# ==============================================================================
Import-Module ActiveDirectory

$PDC = (Get-ADDomainController -Discover -Service PrimaryDC).HostName
Write-Output "Connecting to Primary Domain Controller (PDC Emulator): $PDC"

# Inspect current KRBTGT password metadata
$KrbtgtAccount = Get-ADUser -Identity "krbtgt" -Server $PDC -Properties PasswordLastSet, "msDS-KrbTgtHistory"
Write-Output "Current KRBTGT Password Last Set: $($KrbtgtAccount.PasswordLastSet)"

# Generate a cryptographically secure 128-character password
Add-Type -AssemblyName System.Web
$NewPassword = [System.Web.Security.Membership]::GeneratePassword(128, 32)
$SecurePassword = ConvertTo-SecureString $NewPassword -AsPlainText -Force

# Execute Step 1: Set new password on PDC
Write-Output "Resetting KRBTGT account password on PDC Emulator..."
Set-ADAccountPassword -Identity "krbtgt" -NewPassword $SecurePassword -Server $PDC

# Force Forest-Wide Immediate Active Directory Replication
Write-Output "Triggering urgent AD replication across all Domain Controllers..."
repadmin /syncall $PDC /d /e /a /P

# Verify replication status across all DCs
$DomainControllers = Get-ADDomainController -Filter *
foreach ($DC in $DomainControllers) {
    $DCKrbtgt = Get-ADUser -Identity "krbtgt" -Server $DC.HostName -Properties PasswordLastSet
    Write-Output "DC: $($DC.HostName) | KRBTGT PasswordLastSet: $($DCKrbtgt.PasswordLastSet)"
}

Write-Warning "Step 1 Complete! Wait 12-24 hours for all existing TGT tickets to renew naturally before executing Step 2."
9. Production Implementation Phases & Rollout Roadmap
Rolling out Kerberos FAST and Protected Users across an enterprise environment with thousands of servers must follow a disciplined, four-phase rollout to avoid breaking legacy operational tooling:
- Phase 1: Discovery & Auditing (Days 1 – 14): Deploy the KDC GPO in Supported mode. Collect Event ID 4768 and 4769 logs in your SIEM to catalog all clients and service accounts still utilizing RC4 or legacy unarmored pre-authentication.
- Phase 2: Service Account Migration to gMSA (Days 15 – 30): Convert all high-privilege service accounts (SQL, IIS, Scheduled Tasks) to Group Managed Service Accounts (gMSA). Verify that no humans are logging into service accounts interactively.
- Phase 3: Protected Users Group Enrollment (Days 31 – 45): Enroll Enterprise Admins, Domain Admins, and Schema Admins into Protected Users. Validate that administrative workflows (PowerShell remoting, RSAT) function properly over Kerberos without NTLM fallbacks.
- Phase 4: Enforcement & Armor Lock (Day 46+): Switch the KDC GPO to Enforced mode and configure Domain Controllers to reject any unarmored Kerberos authentication requests.
7. Comprehensive Kerberos Diagnostic Scenarios
| Event ID / Code | Diagnostic Description | Root Cause & Engineering Resolution |
|---|---|---|
KRB_AP_ERR_SKEW (0x25) |
Clock skew between Domain Controller and client machine exceeds maximum tolerance (default 5 minutes). | Synchronize time via NTP. Ensure all domain workstations sync with Domain Controllers via w32tm /resync /rediscover. Verify DC PDC Emulator is synchronized with an external stratum-1 NTP source. |
KDC_ERR_C_PRINCIPAL_UNKNOWN (0x06) |
Client username does not exist in Active Directory database. | Check for typos in UPN or sAMAccountName. In multi-domain forests, verify Global Catalog replication status and ensure the user’s UPN suffix is registered in Active Directory Domains and Trusts. |
KDC_ERR_S_PRINCIPAL_UNKNOWN (0x07) |
The target Service Principal Name (SPN) could not be located in the directory. | Register the missing SPN using setspn -S service/hostname domainccount. Ensure the service hostname matches the fully qualified domain name (FQDN) used by client applications. |
Event ID 4625 (Substatus 0xC000006A) |
Logon failure: User entered an invalid password. | If recurring for a specific service account, check for hardcoded legacy scripts, scheduled tasks, or stale Windows Credential Manager entries attempting automated authentications. |
7. Production Checklist & Recommendations
- Deploy Kerberos FAST in Supported mode first, monitor Event ID 4768 for armored tickets, then transition to Enforced mode.
- Place all Domain Admins, Schema Admins, and Enterprise Admins into the Protected Users group immediately.
- Never log into user-facing Tier-1 or Tier-2 machines with Tier-0 credentials; mandate Privileged Access Workstations (PAWs).
- Rotate the
KRBTGTforest password twice per year using the Microsoft Dual-Run KRBTGT reset script to invalidate golden tickets.
Authoritative Technical References & Implementation Guides
Standards, official architecture centers, and verified documentation for this production workload: