
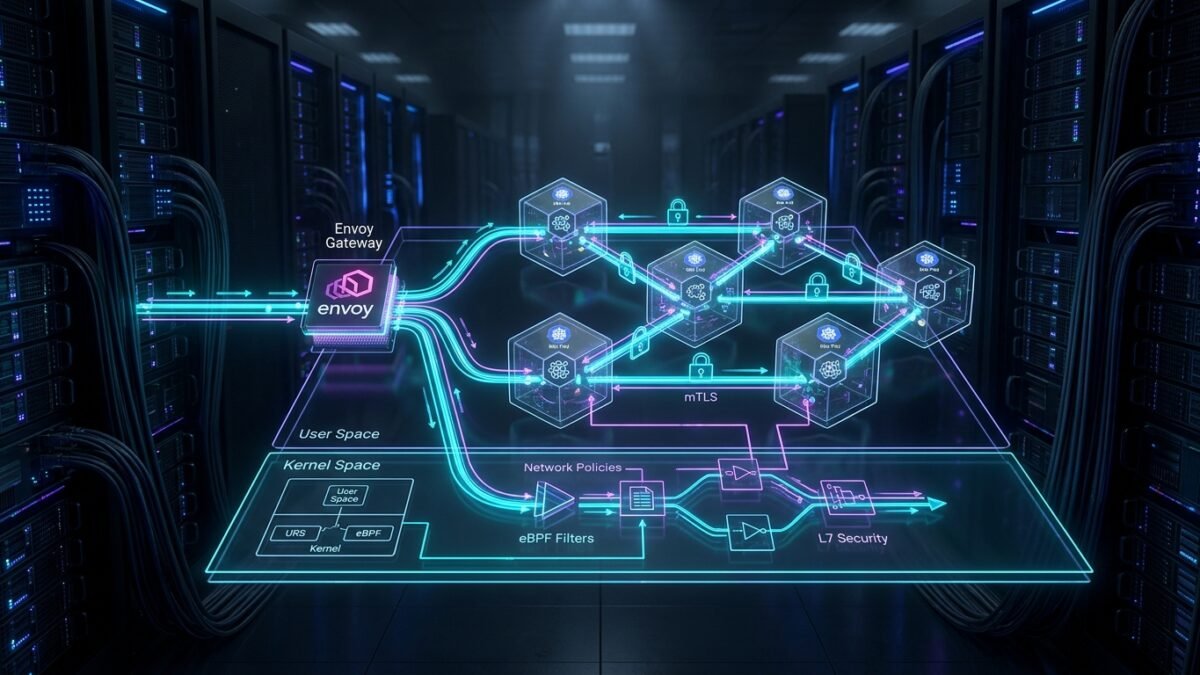
Traditional Kubernetes Ingress controllers relying on legacy iptables and user-space NGINX sidecars introduce severe latency bottlenecks and expand the cluster attack surface. In modern production environments, migrating to the Kubernetes Gateway API powered natively by Cilium eBPF transforms the Linux kernel into an ultra-high-speed, identity-aware ingress and service mesh engine. This deep dive delivers a production blueprint for deploying Cilium Gateway API, enforcing cryptographically verified SPIFFE/SPIRE mTLS at Layer 7, and eliminating lateral pod traversal with zero-overhead kernel filtering.
1. Why Traditional Ingress-NGINX Fails in Large-Scale Clusters
As Kubernetes clusters scale beyond hundreds of services and tens of thousands of pods, traditional ingress architectures face systemic performance and operational limits:
- iptables O(N) Complexity: Every new service and endpoint appends rules to the node’s iptables chain. Packet evaluation becomes sequentially slower as rule counts scale.
- Sidecar Memory Bloat: Running Envoy or Linkerd sidecars alongside every microservice pod consumes significant CPU and RAM, dramatically increasing cloud compute bills.
- Lack of Native Layer 7 Network Policies: Standard Kubernetes NetworkPolicies only filter traffic at Layer 3/4 (IP and port). They cannot inspect HTTP paths, methods, or headers without an external proxy layer.
2. Architectural Shift: Cilium eBPF & Kubernetes Gateway API
By leveraging extended Berkeley Packet Filter (eBPF), Cilium hooks directly into the Linux socket layer and network interface queue (tc/XDP), routing packets at bare-metal speeds before they hit the Linux network stack. Through the Gateway API, Cilium provisions an embedded Envoy proxy instance dynamically only at ingress boundaries, managing traffic with declarative Gateway and HTTPRoute CRDs.
3. Production Cilium Helm Installation with Gateway API & mTLS
Deploy Cilium using Helm 3 with eBPF host routing, Gateway API, and SPIRE-backed mutual TLS enabled:
# Step 1: Install Gateway API CRDs v1.1.0
kubectl apply -f https://github.com/kubernetes-sigs/gateway-api/releases/download/v1.1.0/standard-install.yaml

# Step 2: Deploy Cilium CNI with Gateway API, L7 Proxy & mTLS
helm repo add cilium https://helm.cilium.io/
helm repo update

helm upgrade --install cilium cilium/cilium --version 1.16.1
  --namespace kube-system
  --set kubeProxyReplacement=true
  --set gatewayAPI.enabled=true
  --set authentication.mutual.spire.enabled=true
  --set authentication.mutual.spire.install.enabled=true
  --set l7Proxy=true
  --set hubble.enabled=true
  --set hubble.relay.enabled=true
  --set hubble.ui.enabled=true
4. Declarative Gateway & Zero-Trust HTTPRoute Manifests
Define an enterprise gateway that terminates TLS using cert-manager secrets and routes traffic to internal microservices with strict header and path matching:
apiVersion: gateway.networking.k8s.io/v1
kind: Gateway
metadata:
  name: production-gateway
  namespace: ingress-system
spec:
  gatewayClassName: cilium
  listeners:
  - name: https
    protocol: HTTPS
    port: 443
    tls:
      mode: Terminate
      certificateRefs:
      - name: wildcard-cloudknowledge-tls
    allowedRoutes:
      namespaces:
        from: Selector
        selector:
          matchLabels:
            ingress-enabled: "true"
---
apiVersion: gateway.networking.k8s.io/v1
kind: HTTPRoute
metadata:
  name: payment-api-route
  namespace: payments
spec:
  parentRefs:
  - name: production-gateway
    namespace: ingress-system
  hostnames:
  - "api.cloudknowledge.in"
  rules:
  - matches:
    - path:
        type: PathPrefix
        value: /v2/payments
      method: POST
    backendRefs:
    - name: payment-service
      port: 8080
5. Enforcing Layer 7 CiliumNetworkPolicy
Block all unauthorized traffic between namespaces and enforce HTTP method verification directly inside the kernel:
apiVersion: cilium.io/v2
kind: CiliumNetworkPolicy
metadata:
  name: secure-payment-ingress
  namespace: payments
spec:
  endpointSelector:
    matchLabels:
      app: payment-service
  ingress:
  - fromEndpoints:
    - matchLabels:
        io.kubernetes.pod.namespace: ingress-system
        cilium.io/ingress: "true"
    toPorts:
    - ports:
      - port: "8080"
        protocol: TCP
      rules:
        http:
        - method: "POST"
          path: "/v2/payments.*"
  authentication:
    mode: required
6. Real-Time Packet Forensics via Hubble CLI
Validate that policy enforcement and mTLS handshakes are executing successfully in the kernel without packet drops:
# Monitor real-time L7 traffic and mTLS authentication state
hubble observe --namespace payments --follow --protocol http
  --output jsonpb | jq '{src: .flow.source.pod_name, dst: .flow.destination.pod_name, verdict: .flow.verdict, auth: .flow.auth_type}'