
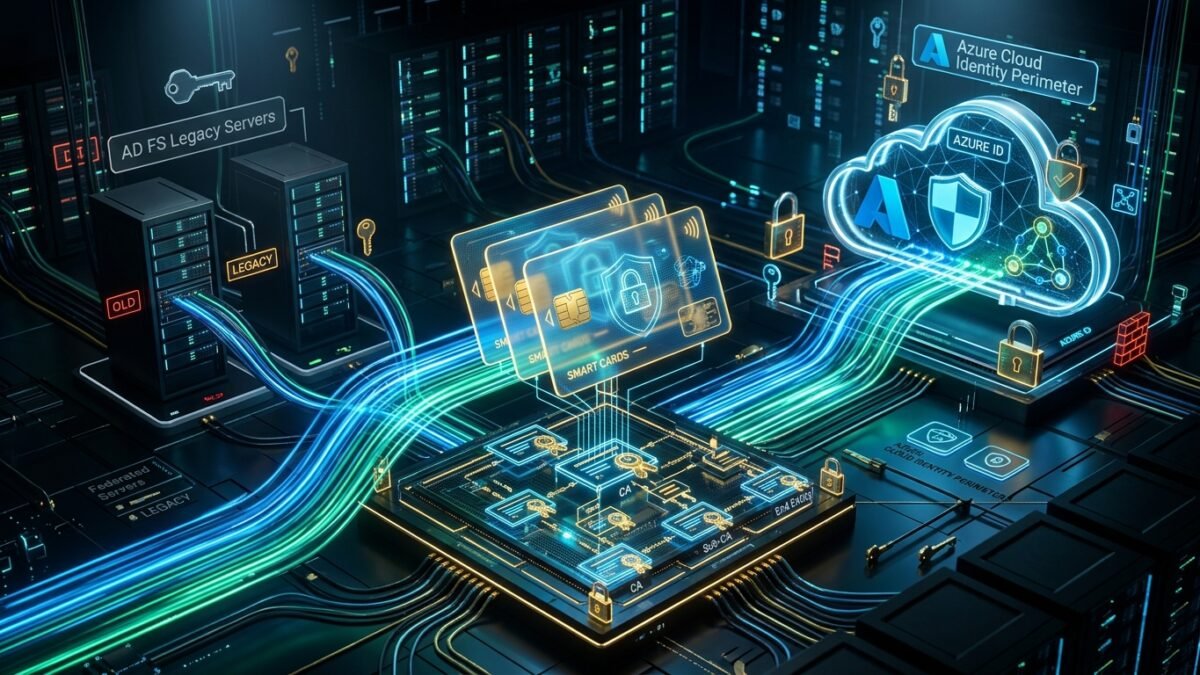
Decommissioning on-premises Active Directory Federation Services (AD FS) in favor of native cloud authentication is a foundational milestone for Zero Trust identity posture. However, organizations relying on US Government PIV cards, CAC cards, or hardware Smart Cards (YubiKey PIV) frequently find themselves anchored to legacy AD FS farms solely due to client certificate inspection. In this architectural guide, we break down how to migrate mission-critical Certificate-Based Authentication (CBA) directly to Microsoft Entra ID—eliminating on-prem federation vulnerabilities, deprecating public AD FS proxy endpoints, and establishing cryptographically enforced Conditional Access authentication strengths.
1. The Problem: The Security Burden of Legacy AD FS Farms
For over a decade, AD FS was the de facto standard for federating on-premises PKI certificates with Office 365 and cloud workloads. However, maintaining multi-tier AD FS architectures introduces severe operational and security overhead:
- Golden SAML Vulnerabilities: Compromise of an AD FS token-signing certificate enables adversaries to forge SAML assertions with arbitrary claims, bypassing MFA and cloud logs entirely.
- Perimeter Attack Surface: Web Application Proxies (WAP) must remain publicly exposed to port 443, making them recurring targets for credential stuffing and unpatched zero-day exploits.
- Complex High Availability: Maintaining Geo-redundant SQL backends, Windows NLB/F5 hardware load balancers, and continuous CRL distribution sync demands substantial engineer overhead.
| Feature / Dimension | Legacy AD FS Smart Card Auth | Native Microsoft Entra CBA |
|---|---|---|
| Token Issuance Authority | On-prem AD FS Token-Signing Cert | Microsoft Entra Security Token Service (STS) |
| Perimeter Infrastructure | WAP DMZ proxies + AD FS farm servers | Zero on-prem web servers required |
| CRL Revocation Checking | Direct LDAP / HTTP from AD FS servers | Microsoft Entra Cloud CRL caching engine |
| Conditional Access Enforcement | Coarse-grained claim rules / regex | Granular, real-time risk & device posture checks |
2. Architectural Blueprint: Native Microsoft Entra CBA
Microsoft Entra Certificate-Based Authentication allows clients to present X.509 certificates directly to Microsoft Entra STS (https://certauth.login.microsoftonline.com). The cloud service validates the certificate chain against pre-uploaded Root and Intermediate Certification Authorities (CAs), checks the Certificate Revocation List (CRL), and maps certificate attributes to user accounts in Entra ID.
Certificate Binding Rules
Entra CBA supports two principal binding modes:
- PrincipalName (High Affinity): Maps the Subject Alternative Name (SAN) Principal Name directly to
userPrincipalNameoronPremisesUserPrincipalName. Required for multi-factor authentication (MFA) classification under Entra Authentication Strengths. - RFC822Name / SubjectKeyIdentifier (Low Affinity): Used for email address matching or legacy token hardware mapping. Classified as single-factor unless paired with secondary credentials.
3. Step-by-Step Implementation: Uploading PKI Chains via Microsoft Graph PowerShell
To establish trust between Microsoft Entra ID and your Enterprise PKI (Active Directory Certificate Services or HashiCorp Vault), execute the following PowerShell 7 script using Microsoft Graph SDK v2:
# Step 1: Connect to Microsoft Graph with Directory.AccessAsUser.All privileges
Connect-MgGraph -Scopes "Organization.ReadWrite.All", "Directory.AccessAsUser.All"

# Step 2: Extract Base64 raw bytes of Enterprise Root and Subordinate CAs
$rootCert = [System.Security.Cryptography.X509Certificates.X509Certificate2]::new("C:PKIEnterpriseRootCA.cer")
$subCert  = [System.Security.Cryptography.X509Certificates.X509Certificate2]::new("C:PKIEnterpriseSubCA.cer")

# Step 3: Define Certificate Authority Payloads
$rootCaConfig = @{
    "@odata.type" = "#microsoft.graph.certificateAuthority"
    isRootAuthority = $true
    certificate = [System.Convert]::ToBase64String($rootCert.RawData)
    certificateRevocationListUrl = "http://crl.contoso.com/crl/EnterpriseRootCA.crl"
}

$subCaConfig = @{
    "@odata.type" = "#microsoft.graph.certificateAuthority"
    isRootAuthority = $false
    certificate = [System.Convert]::ToBase64String($subCert.RawData)
    certificateRevocationListUrl = "http://crl.contoso.com/crl/EnterpriseSubCA.crl"
    deltaCertificateRevocationListUrl = "http://crl.contoso.com/crl/EnterpriseSubCA+.crl"
}

# Step 4: Post Certificate Authorities to Entra Tenant Configuration
$certAuthorities = @($rootCaConfig, $subCaConfig)
Update-MgOrganizationCertificateBasedAuthConfig -OrganizationId (Get-MgOrganization).Id -CertificateAuthorities $certAuthorities

Write-Host "Successfully registered PKI Trust Chain in Microsoft Entra ID." -ForegroundColor Green
4. Configuring Authentication Strengths in Conditional Access
Once the trust chain is established, configure an Authentication Strength to mandate Phishing-Resistant MFA across all privileged administrative roles and corporate workstations:
- Navigate to Microsoft Entra Admin Center > Protection > Authentication Methods > Certificate-based authentication.
- Set the status to Enabled for your target pilot security group.
- Under Configure, select Multi-factor authentication for certificates where SAN matches
userPrincipalName. - Under Protection > Conditional Access > Authentication Strengths, create a custom policy titled
Phishing-Resistant CBA & FIDO2, selecting Certificate-Based Authentication (Multifactor). - Assign this policy to your cloud apps (Exchange Online, SharePoint, Azure Management) to enforce smart card authentication.
5. Troubleshooting Matrix: Common Entra CBA Error Codes
| Error Code | Diagnostic Symptom | Root Cause & Resolution Command |
|---|---|---|
AADSTS50017 |
Certification validation failed | CRL endpoint unreachable from Microsoft Cloud or CRL has expired. Verify your CDP URL is accessible over public HTTP (port 80) without basic auth. |
AADSTS50008 |
SAML / Token validation exception | User account contains mismatched SAN attribute. Check Get-MgUser -UserId user@contoso.com | Select UserPrincipalName, OnPremisesUserPrincipalName. |
AADSTS70043 |
Smart card prompt does not trigger | Client browser is accessing login.microsoftonline.com without TLS client certificate request. Ensure connection redirects to certauth.login.microsoftonline.com. |